
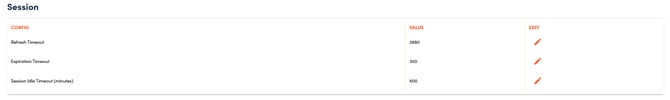
Expiration Timeout (minutes)
This section allows the System Administrator to set how frequently the user token verifies that a user has the right to do what they are trying to do within the RocketDocs platform. If it is within the time frame of the refresh time out (described above), the system verifies the token and allows the user to proceed without having to log in again. The Expiration Timeout always needs to be less than the Refresh Timeout.
Refresh Timeout (minutes)
This section allows the System Administrator to set how frequently the session will refresh the token that is assigned to the current/new session. If a user leaves the application (closes the tab in a web browser) and comes back within the timeframe specified here, the current authenticated token will be refreshed, and the session will continue. If the user leaves the application and comes back after the time specified here, the user will need to log back into the application and it will provide a new token for the session. The Refresh Timeout value always needs to be greater than the Expiration Timeout.
Session Idle Timeout (minutes)
This section allows the System Administrator to set how long it takes the system to log out a user due to inactivity while the application is still open in a web browser tab. When the time limit is hit, the system will prompt the user to confirm that they would like to remain logged in and if the user does not respond within 30 seconds, they will be logged out. This applies to the web application and LaunchPad.
📋 Note:
Setting this section to 0 turns Session Idle Timeout off.